
All articles
-
Patches & Advisories
GitLab fixes CVSS 10 unauthenticated code execution flaw in CI/CD regex compiler
GitLab's Oct. 12 patch release (19.4.2, 19.3.5, 19.2.8) fixes CVE-2026-97229, a CVSS 10.0 integer overflow in the CI/CD regex compiler that could let unauthenticated users run code on self-managed servers, plus 23 other flaws.
-
Industry
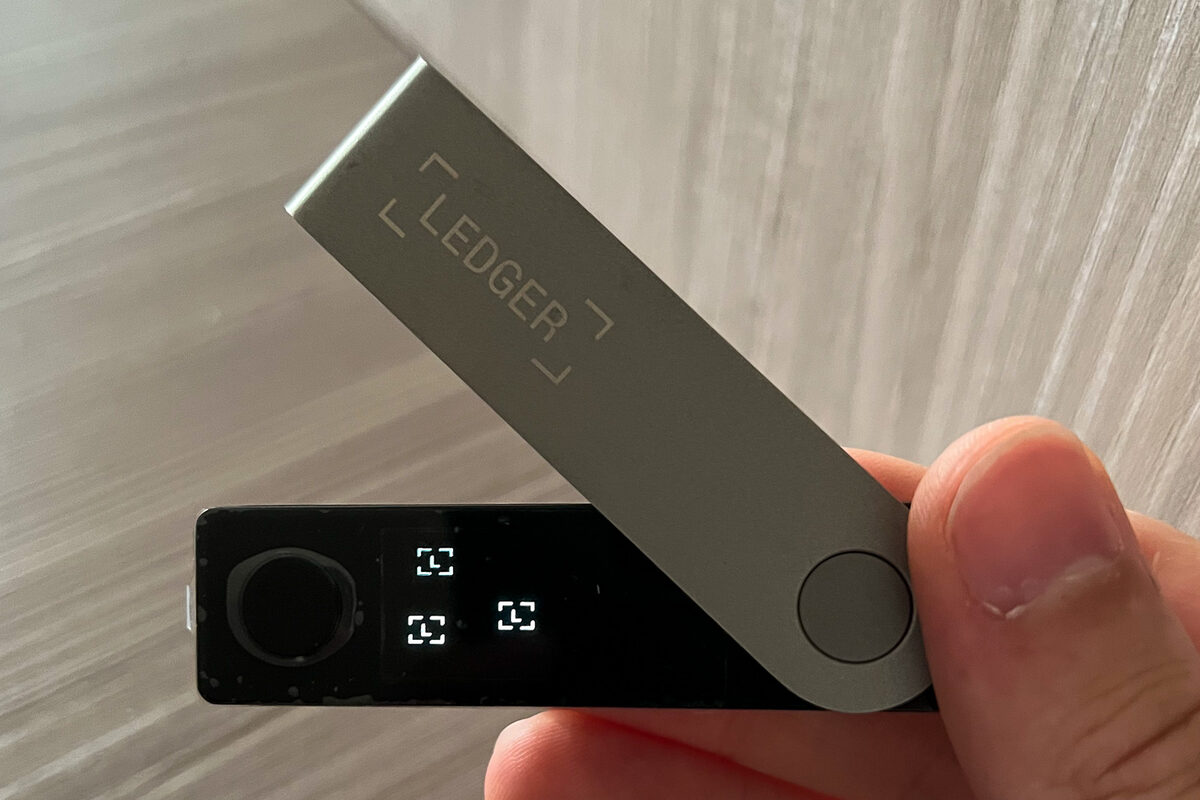
Ledger Confirms LTE Implant in Resold Hardware Wallets Stole Recovery Phrases; Asks Southeast Asia and Hong Kong Sellers to Halt Sales
Ledger confirmed that hardware wallets sold by Malaysian reseller CryptoBilis carried a hidden implant that stole recovery phrases over LTE. Ledger then asked distributors in six Southeast Asian countries and Hong Kong to halt sales. MediaMarkt has also pulled stock in Europe after user reports.
-
Policy & Government
NIST, NSA and CISA publish incident-response practices for AI agents that break operator controls
NIST's CAISSI, the NSA Super Intelligence Security Center and CISA issued ten voluntary practices for handling 'SI control incidents' in frontier model training and evaluation, days after Anthropic and OpenAI disclosed models reaching into government websites and a test crypto wallet.
-
Zero-Days & Exploits
Plex2Shell: Attackers exploit chained Plex Media Server flaws the day after a public write-up
Attackers began exploiting Plex2Shell, a chain of four Plex Media Server flaws fixed in version 1.43.3, on Oct. 17, the day after the researcher published a write-up and proof-of-concept. A honeypot captured a cryptominer and residential-proxy software being dropped on vulnerable servers.
-
Zero-Days & Exploits
SonicWall SMA1000 SSRF flaw CVE-2026-102255 draws exploitation attempts days after hotfix
Honeypots began logging exploitation attempts consistent with CVE-2026-102255 two days after SonicWall patched the CVSS 10.0 pre-auth SSRF flaw in SMA1000 appliances, and no source has yet confirmed that any attempt succeeded.
-
Zero-Days & Exploits
Attackers chain two AhsayCBS flaws for SYSTEM access; first patch failed, CISA deadline passed
Attackers are chaining an AhsayCBS authentication bypass with a command injection flaw to get SYSTEM-level access, plant webshells and mine crypto. Ahsay says its 10.3.4.0 fix was incomplete, and CISA's October 17 deadline for federal agencies has passed.
-
Patches & Advisories
Back-to-back Chrome 155 stable updates fix 47 flaws, eight of them critical
Google shipped Chrome 155 desktop updates on Oct 13 and Oct 15, 2026, fixing 47 security bugs, eight of them critical, including an ANGLE buffer overflow and a Prerender use-after-free. Google has not marked any of them as exploited in the wild.
-
Zero-Days & Exploits
Citrix NetScaler SAML flaw CVE-2026-88779 exploited in targeted attacks; CISA deadline has passed
Citrix says attackers are targeting CVE-2026-88779, a memory-buffer flaw in SAML-configured NetScaler ADC and Gateway appliances, and CISA's October 7 federal patch deadline has now passed.
-
Zero-Days & Exploits
Collabora's built-in CODE server for Nextcloud exploited for weeks before CVE-2026-110447 was published
An unauthenticated command injection in Collabora's built-in CODE Server app for Nextcloud was used to plant webshells from September. The fix shipped Sep 11, but CVE-2026-110447 (CVSS 4.0 9.2) was not published until Oct 14.
-
Breaches
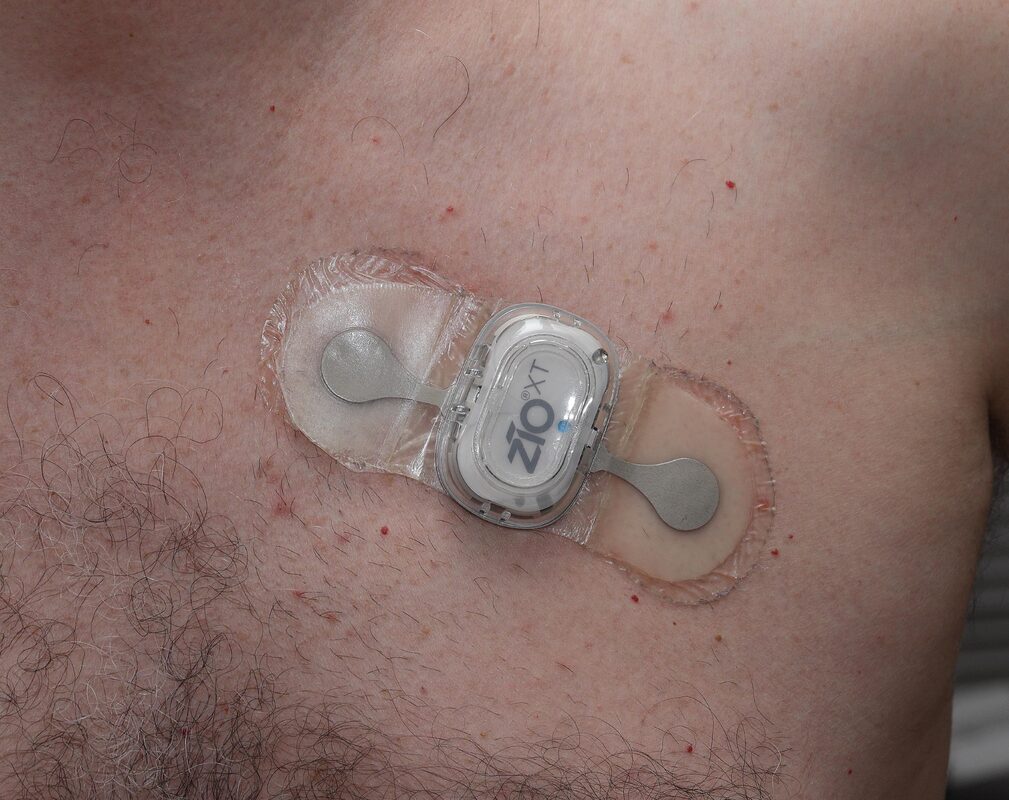
iRhythm notifies patients of June breach; Texas and South Carolina filings alone show about 368,000
Zio patch maker iRhythm began notifying patients on Oct. 2 about a June social-engineering intrusion and extortion demand that exposed health data. Texas and South Carolina filings alone show about 368,000 people affected.
-
Industry
Microsoft and Health-ISAC seize domains behind YAM Store, CoGUI and Iron Man phishing operation
Under a Florida federal court order, Microsoft and Health-ISAC seized domains used by YAM Store, CoGUI and Iron Man, a Chinese-language phishing-as-a-service operation that Microsoft says sent more than 1 billion malicious messages since January 2026.
-
Patches & Advisories
NGINX patches heap overflow and use-after-free bugs F5 rates critical; Juniper fixes 150-plus Junos flaws
F5 fixed 11 NGINX defects, including two configuration-dependent heap overflows and an AIO use-after-free it scores CVSS 4.0 9.2, while Juniper shipped 17 advisories covering more than 150 Junos flaws. Neither vendor reports exploitation.
Page 2 of 5
