
All articles
-
Ransomware
Winona County says spring ransomware attack exposed SSNs, fingerprints and DNA paternity reports
Winona County, Minn., began mailing breach letters October 8 for an April ransomware attack. Intruders copied data including SSNs, fingerprints and DNA paternity-test reports. The county has not said whether it paid a ransom this time or how many people were affected.
-
Patches & Advisories
Android's October 2026 bulletin fixes 25 flaws, seven of them critical, in one patch level
Google's October 2026 Android Security Bulletin fixes 25 vulnerabilities in Framework and System under the single patch level 2026-10-01. Seven are rated critical, including four local privilege escalation bugs in Android 16 and 17. Google does not flag any of them as exploited in the wild.
-
Zero-Days & Exploits
Apple's Sept. 28 updates fix CoreGraphics zero-day CVE-2026-86950, possibly exploited against targeted iOS users
Apple's September 28 updates fix CVE-2026-86950, a CoreGraphics out-of-bounds write that Apple says may have been exploited against specific targeted people on iOS versions before iOS 27. CISA's October 13 federal deadline has passed.
-
Breaches
Astrana Health files Item 1.05 8-K over impersonation calls that spoofed its main phone number
Astrana Health told the SEC that threat actors impersonated staff and spoofed its main corporate phone number in an effort to get system access, and that confidential data was likely accessed or taken. No patient count has been released.
-
Policy & Government
CISA sends final CIRCIA rule to White House review: 72-hour incident and 24-hour ransom-payment reports
CISA sent its final CIRCIA incident-reporting rule to OMB on October 1, 2026. The 2024 proposal would cover about 316,000 critical-infrastructure entities, which would report incidents within 72 hours and ransom payments within 24 hours. White House review could push publication into early 2027.
-
Zero-Days & Exploits
Exploited Cisco Catalyst SD-WAN Manager flaw CVE-2026-76504 gives unauthenticated admin API access
Cisco says attackers are exploiting CVE-2026-76504 (CVSS 9.8), a URI-encoding authentication bypass in Catalyst SD-WAN Manager that grants unauthenticated admin-level API access. There is no workaround. CISA's October 3 federal patch deadline has passed.
-
Zero-Days & Exploits
Citrix NetScaler zero-day CVE-2026-88771 moves to mass exploitation after PoC; CVE-2026-88772 also exploited
Two NetScaler ADC and Gateway flaws rated CVSS v4 9.5 were exploited before disclosure; CVE-2026-88771 was then attacked widely after a public PoC. Responders found stolen config archives and webshells, and CISA's September 30 deadline has passed.
-
Zero-Days & Exploits
FortiMail zero-day CVE-2026-104286 allows unauthenticated file writes; CISA's 3-day deadline has passed
Fortinet says CVE-2026-104286 has been exploited in the wild. The flaw is a CVSS 9.8 path traversal bug in FortiMail that lets unauthenticated attackers write arbitrary files. CISA's October 4 deadline for federal agencies has passed.
-
Industry
IonQ agrees to buy zero-trust firm Elisity in all-stock deal worth up to $1.3 billion
IonQ has signed a deal to buy microsegmentation company Elisity for $1.15 billion in stock plus up to $150 million in earnouts. It plans to combine Elisity's identity-based segmentation with its post-quantum cryptography and QKD business. The deal is expected to close in Q4 2026.
-
Breaches
Upbound mails breach notices for July cloud-file theft after 8-K cited "non-sensitive" data
Upbound Group, parent of Rent-A-Center and Acima, began mailing breach notices on September 23 for files taken from its cloud apps on July 3–6, after a July 21 8-K said "non-sensitive" customer information was obtained in undated incidents.
-
Patches & Advisories
Adobe patches CVSS 10 'BlockStrap' flaw in Adobe Commerce and Magento; Sansec expects exploits to follow
Adobe's APSB26-153 fixes CVE-2026-103849, an unauthenticated CVSS 10.0 template-injection flaw in Adobe Commerce and Magento that Sansec calls BlockStrap; Adobe knows of no exploits, but Sansec expects attacks and says stores also need September's hotfix.
-
Patches & Advisories
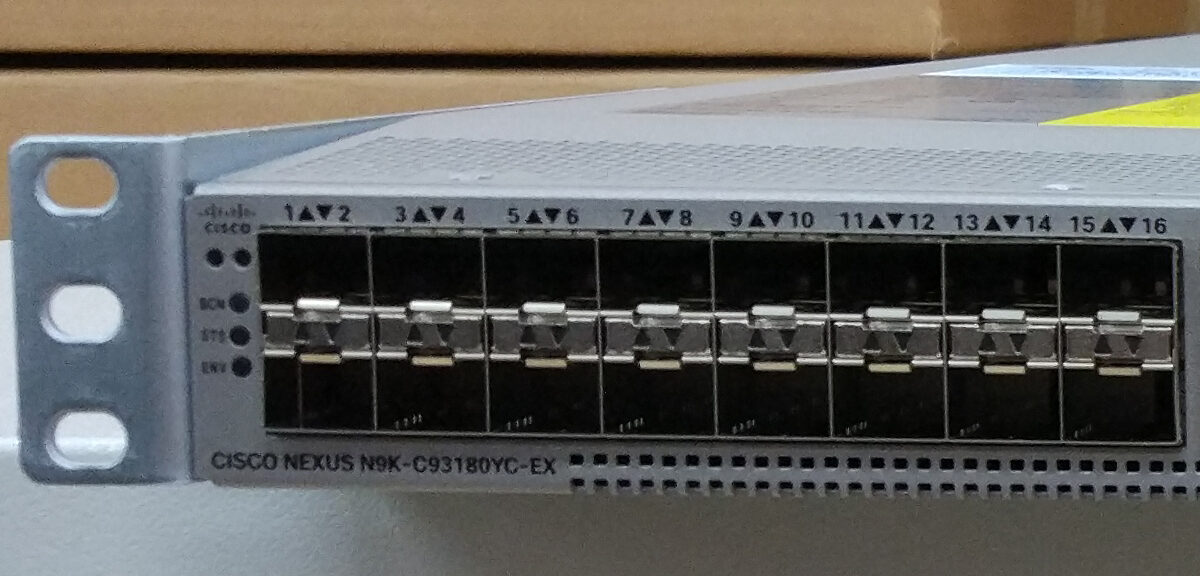
Cisco fixes five critical Nexus NX-OS flaws and a CVSS 10.0 bug in License On-Prem
Cisco has fixed five critical NX-OS flaws in Nexus 3000 and 9000 switches that can be reached when NX-API, NGOAM or MPLS OAM is enabled, plus four License On-Prem bugs rated as high as CVSS 10.0.
Page 1 of 5
