
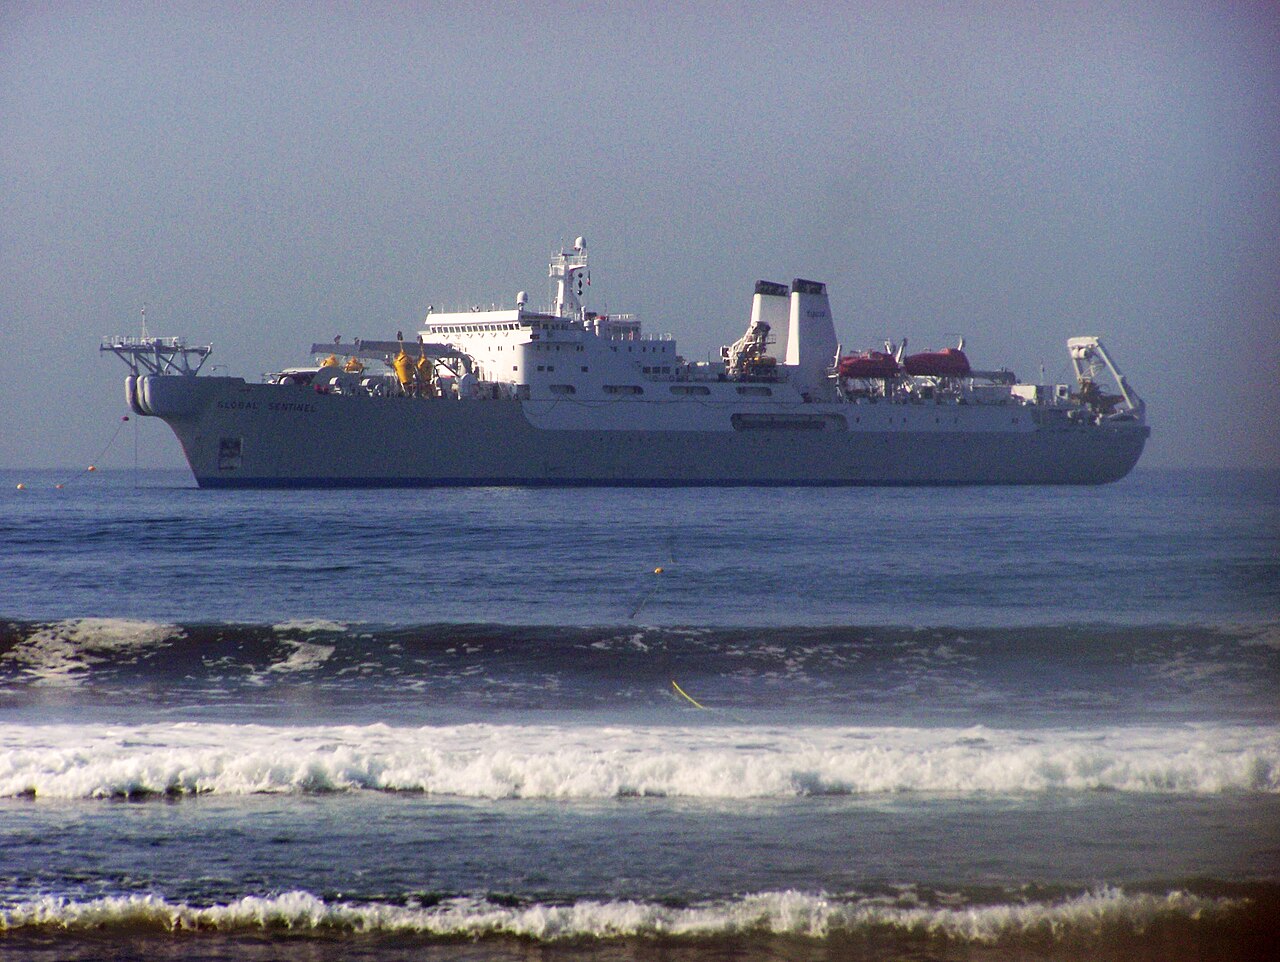
For more than a century, the main UK law against damaging the cables on the seabed has been the Submarine Telegraph Act 1885. It was written when "submarine cable" meant a copper telegraph line. According to The Record, it carries a maximum fine of GBP 1,000 and five years' imprisonment in cases of deliberate damage. The cables the new proposals cover carry about 99% of the UK's international data, the government says, and undersea pipelines supply 74% of the country's gas.
The Department for Digital, Culture, Media and Sport (DCMS) wants to change that. In a White Paper announced on 22 October 2026, the government proposes much longer prison terms, unlimited fines and a new set of legal security duties for the companies that own and run subsea telecoms infrastructure. Below we cover what is proposed, why now, and who should be paying attention.
What exactly is being proposed?
The White Paper sets penalties by the intent behind the damage. As reported by The Record:
- Up to 14 years in prison for deliberate damage to undersea cables and pipelines.
- Up to 10 years for reckless damage.
- Up to 2 years for damage caused by gross negligence.
On top of the custodial sentences, the government's release says the proposals include unlimited fines for those who intentionally, recklessly or negligently damage the infrastructure. Help Net Security reports that the plans include unlimited fines for ship owners whose vessels damage the infrastructure. The government itself says that where cable faults occur, they are due to accidents involving anchors or trawler nets being dragged across the cables, environmental hazards or technical failures.
The package goes beyond criminal penalties. The government also proposes:
- Statutory security and resilience duties for subsea telecoms providers, including stronger requirements to identify and manage risks to their networks.
- Government powers to intervene and direct telecoms providers, including cable and repair providers, where national security is at risk.
- New rules covering fiber-optic sensing, according to The Record. This technology can detect activity at sea, but the government warns it could pose national security risks if sensitive data fell into the wrong hands.
Help Net Security describes the White Paper as an update to laws that in some cases date back 140 years.
Why now?
The government links the crackdown to what it calls suspicious Russian activity around critical undersea infrastructure. Its release says that in April the British Armed Forces exposed a covert Russian submarine operation around critical undersea infrastructure in and around UK waters, and Help Net Security repeats the point. Telecoms Minister Ian Murray is quoted in the coverage in support of the measures. The attribution to Russia comes from the UK government. The sources do not tie any particular cable-damage incident to a criminal conviction.
The cost argument is easy to make. The Record points to Estlink 2, an electricity cable between Finland and Estonia damaged by the anchor of the Eagle S oil tanker on Christmas Day 2024, where grid operator Elering estimated repairs at EUR 50 to 60 million. The Record describes the old law's GBP 1,000 maximum fine as a fraction of repair costs. The Record also notes that officials from several North Sea and Baltic countries later said they increasingly believed that incident and other Baltic Sea cable breaks were accidental, and that questions over jurisdiction and over whether incidents were reckless accidents or deliberate have complicated prosecutions elsewhere.
Is this law yet?
No. A White Paper is a policy proposal: it sets out what the government intends to legislate. Its publication opens a 12-week public consultation, which The Record says closes on 14 January 2027. The sentencing tiers, fine levels and operator duties described here could still change before any bill is passed. The direction is clear, but organizations should treat the details as proposals until legislation appears.
Why the three tiers matter
The split between deliberate, reckless and grossly negligent damage addresses a specific problem. As The Record's reporting on past incidents shows, it can be hard to establish whether damage was an accident or a deliberate act. A system that only punishes proven sabotage leaves little room to act when intent is unclear. Adding reckless and gross-negligence offenses, with penalties of up to 10 and 2 years, and providing for unlimited fines on ship owners, suggests prosecutors would not need to prove deliberate sabotage to secure a meaningful sanction. That is our reading of the proposal rather than a claim made in the sources. The financial exposure would also fall on shipowners, not just individuals.
The fiber-optic sensing rules are a separate strand. The technology can detect activity at sea, which the government sees as both useful and a potential security risk, so the White Paper proposes a separate regulatory regime for it.
What It Means for Defenders
This is a policy change, not a vulnerability. There is nothing to patch and no version to upgrade. It still matters to several groups:
- Subsea telecoms operators and landing-station owners are directly affected. The proposed statutory security and resilience duties would add compliance obligations, and the government would gain powers to intervene on national-security grounds. Operators should read the White Paper, map their current physical-security, monitoring and incident-response practices against it, and get ready to take part in the consultation. Anyone already using or considering fiber-optic sensing should watch for the new rules the White Paper describes.
- Shipping companies and vessel owners working in UK waters face a new liability: proposed unlimited fines for intentional, reckless or negligent damage. Anchoring procedures, crew training and route planning near known cable corridors become questions of legal exposure as well as seamanship.
- Enterprises, cloud customers and MSPs are not regulated by these proposals, but they rely on the infrastructure involved. With the government stating that about 99% of UK international data runs over subsea cables, the sensible step is to check your own resilience assumptions. Ask your carriers and cloud providers whether your critical international traffic uses diverse cable paths and landing points. Find out how failover behaves if one route goes down, and include a major cable outage in continuity and tabletop exercises.
- Security and risk teams should treat physical damage to undersea infrastructure as a real threat scenario in risk registers. The UK government is now openly connecting it to hostile state activity, and the Estlink 2 repair estimate shows how expensive such damage can be.
Defenders can't prevent anchor drags. What they can control is how much one damaged cable disrupts their own operations, and redundancy is the main tool for that.
