
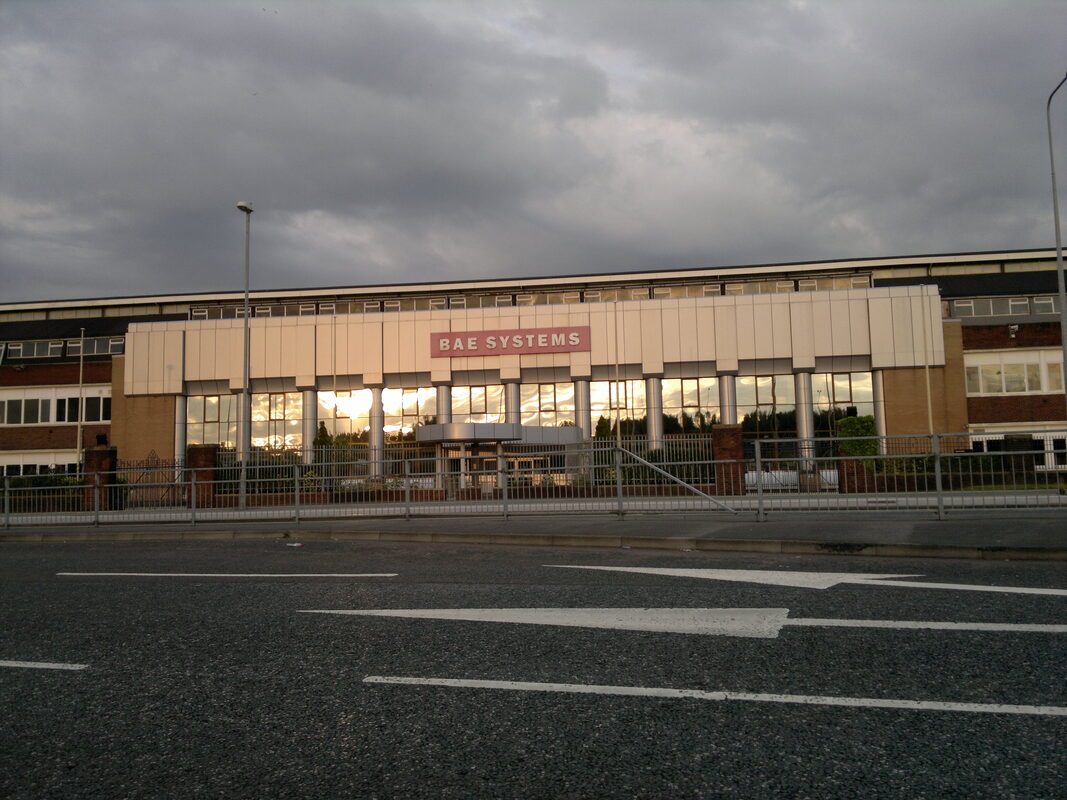
The federal judiciary's system for sending bankruptcy notices has stopped working after a cybersecurity incident at BAE Systems, the contractor that runs it. On Oct. 15, the Administrative Office of the U.S. Courts (AO) said the incident affected BAE Systems IT and the websites that support the Bankruptcy Noticing Center (BNC), which produces and transmits bankruptcy notices for federal bankruptcy courts nationwide. As a result, the BNC has stopped producing and distributing bankruptcy notices.
The AO said all access to the BNC systems and websites BAE operates for the judiciary is unavailable, including bnc.uscourts.gov, bankruptcynotices.uscourts.gov, notices.uscourts.gov, and the National Creditor Registration Service. The AO says it is coordinating with BAE and communicating with the affected courts. Neither organization has said when service will return.
Both the judiciary and the contractor have confirmed the incident. Several things have not been disclosed: whether ransomware was involved, whether any threat group has claimed the attack, and what kind of intrusion it was. According to The Record, the AO did not respond to questions about the nature of the incident or whether data was stolen. ZeroDayFeed found no public claim of responsibility in the sources reviewed for this article.
What the judiciary and BAE have said
According to the AO, BAE operates the BNC systems and websites on behalf of the federal judiciary. "BAE is actively investigating this incident and working to restore operations," the AO said in its Oct. 15 notice. That notice is the main official source for the outage.
A BAE spokesperson told BleepingComputer: "We are aware of a security incident that is isolated to the BNC system and have taken immediate steps to address it." The spokesperson added that BAE is "coordinating closely" with the AO on the response. The company did not say what those steps were, and it did not say whether any data was accessed or taken.
The Record also reported on Oct. 15 that federal bankruptcy courts were dealing with outages after the contractor cyberattack, and carried the same BAE statement. That report matches the AO's account. The Record said the Cybersecurity and Infrastructure Security Agency (CISA) referred its questions to the U.S. Courts, and the FBI did not comment.
Why the Bankruptcy Noticing Center matters
The BNC produces and sends the official notices that federal bankruptcy courts across the country issue in their cases. The National Creditor Registration Service, which is tied into that noticing system, is also offline.
When the noticing pipeline stops, the courts keep running, but the system loses one of the main ways it tells people what is happening. The AO's notice does not say how courts will handle notices that come due during the outage. It also does not say whether deadlines tied to notice will be adjusted. People with active cases should look for guidance from their individual court rather than assume a general rule applies.
Part of a pattern for the judiciary
This is not the federal courts' first recent security problem. As BleepingComputer noted, the judiciary said in 2025 that it was strengthening cybersecurity defenses after a cyberattack on its electronic case management systems. BleepingComputer also cited an August 2025 Politico report that hackers had breached CM/ECF, the courts' electronic case management system, and PACER, the federal court document platform.
Nothing in the available reporting connects the BNC incident to that earlier compromise. The two should be treated as separate events unless the judiciary or BAE says otherwise. Together, though, they show that core court infrastructure has been a repeated target. Some of that infrastructure is run directly by the judiciary, and some is run by contractors.
The contractor angle
BleepingComputer describes BAE Systems as Europe's largest defense contractor, which also provides enterprise IT, cloud infrastructure, and cybersecurity services to government agencies. For the defense industrial base and the wider federal contractor community, the incident is a supply-chain example. A government function was disrupted because of a security event at the private company operating it. BAE's statement that the incident is isolated to the BNC system matters, because it suggests the effect did not spread across the company's other operations. That is still the company's own early assessment, and the investigation is ongoing.
Contractors working toward or keeping Cybersecurity Maturity Model Certification (CMMC) will see the issue clearly. When a contractor runs a public-facing service for an agency, the agency's availability depends on the contractor's security. Agencies can outsource operations, but they cannot outsource the outage.
What It Means for Defenders
The incident has no CVE, vendor patch, or published indicators of compromise, so the useful guidance is about process and exposure:
- Bankruptcy practitioners, trustees, and creditors: Expect normal electronic notices to be delayed or missing while the BNC is down. Check case status directly with the relevant court rather than relying on notices. Be skeptical of unexpected messages that claim to be bankruptcy notices, ask for payment, or ask you to "re-register" for notice delivery while official channels are offline. Confirm through the court's own published contact information.
- Organizations registered with the National Creditor Registration Service: The AO and BAE have not said whether any data was exposed. Until they do, watch for targeted phishing that refers to your registration or to specific cases. Treat any credential request tied to these services as suspect.
- Federal contractors running services for agencies: Map which of your systems directly support a government-facing function, and make sure your incident response plan includes notifying and coordinating with that customer agency. Test whether you can isolate an affected environment without taking down unrelated systems. BAE's early claim that the incident is "isolated to the BNC system" is the kind of statement your network segmentation should let you make with confidence.
- Agency and judiciary IT owners: List the public services that depend on a single contractor, and decide in advance how the mission continues if that contractor goes offline. That includes fallback notice methods and how affected parties will be told.
- Everyone: Watch the AO's judiciary news page and BAE's statements for indicators of compromise, scope findings, or a restoration timeline. Update your response when those are published, and do not act on unverified reports.
What remains unknown
Several important questions are still open. The disclosures do not say how the attacker got in, whether the attack involved encryption or data theft, whether personal information about debtors or creditors was exposed, or which courts have been hit hardest by the notice backlog. No group has publicly claimed responsibility, according to the sources reviewed, and neither the judiciary nor BAE has named a responsible actor. ZeroDayFeed will update this story when the AO or BAE releases more details.
Sources
- Cybersecurity Incident Disrupting Bankruptcy Court Operations — Administrative Office of the U.S. Courts, Oct. 15, 2026
- BAE Systems cyberattack disrupts US federal court operations — BleepingComputer, Oct. 16, 2026
- Federal bankruptcy courts dealing with outages after contractor cyberattack — The Record, Oct. 15, 2026
